

CypherLeap
Stand: B642
- | Artificial Intelligence
- | Consultancy
- | IT
- | Security Solutions

CypherLeap is an Australian cybersecurity consultancy helping organisations strengthen their security posture through strategic advisory, managed security services, and offensive security testing. Our team supports businesses across industries with services including ISO 27001, Essential Eight, IRAP, penetration testing, security monitoring, incident response, and cyber risk management. We work closely with organisations of all sizes to deliver practical, business-focused security outcomes that reduce risk, improve compliance, and build resilience against evolving cyber threats.
Practical cybersecurity. Trusted advice. Measurable outcomes.
Address
408/56 Bowman StPyrmont, NSW
2009
Australia
Contact Exhibitor
Products
-
 RADAR+ is CypherLeap's continuous external attack surface and digital risk monitoring service, built on the SOCRadar platform it owns and operates. It finds exposed assets and leaked credentials acros ...
-
 CypherLeap's vCISO gives organisations executive security leadership without a full-time executive salary. A named vCISO runs the security program end-to-end: strategy, board reporting, risk managemen ...
-
 Managed SIEM pairs an industry-leading, vendor-agnostic SIEM platform with senior analysts monitoring 24/7/365. Every alert is triaged by a human before it becomes an incident. CypherLeap reports aver ...
-
 Managed GRC builds an organisation's ISMS from scratch, runs the risk register and policy lifecycle, and prepares it for audit across ISO 27001, Essential Eight, IRAP, APRA CPS 234, PCI DSS and SOC 2. ...
-
 CypherLeap delivers network, application, cloud, and API penetration testing carried out by certified ethical hackers. Engagements go beyond a scan, pairing hands-on offensive testing with actionable ...
-
 Managed IT & Cyber Support unifies IT and cyber operations under one team: endpoint management, identity and access control, cloud infrastructure, and helpdesk services, so clients aren't juggling sep ...
News
-
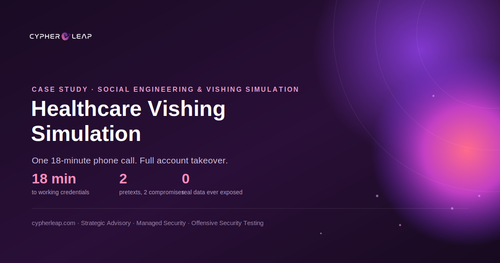 A recent social-engineering simulation run by CypherLeap has shown just how little it can take to compromise a healthcare organisation's IT environment: a phone call, a plausible story, and a service ...