
Virtual CISO
The vCISO's remit runs across six areas. On security strategy, they develop a 12-36 month roadmap aligned to the business's objectives, risk appetite and budget, with reporting built to be board-ready rather than translated after the fact. On board and executive reporting, they deliver monthly or quarterly board packs that turn technical risk into business language, backed by dashboards covering threat posture and compliance status. On risk management, they build and maintain the enterprise risk register, run assessments, and integrate with the organisation's broader enterprise risk management framework. On compliance, they own the program across frameworks like ISO 27001, Essential Eight, APRA CPS 234 and PCI DSS, including audit preparation. On vendor and third-party management, they run security due diligence and vendor risk assessments. And on incident response planning, they develop and test incident response, business continuity and disaster recovery procedures, including annual tabletop exercises for the leadership team.
The engagement runs through four phases:
- Discovery and assessment
- Strategy development
- Ongoing execution and governance
- Reporting with continuous improvement
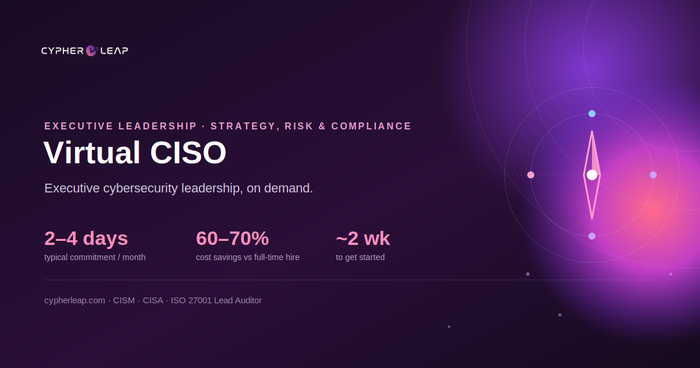
CypherLeap states a typical commitment of 2-4 days a month, cost savings of 60-70% versus a full-time hire, and roughly two weeks to get started.