
Managed SIEM (Security Information and Event Management)
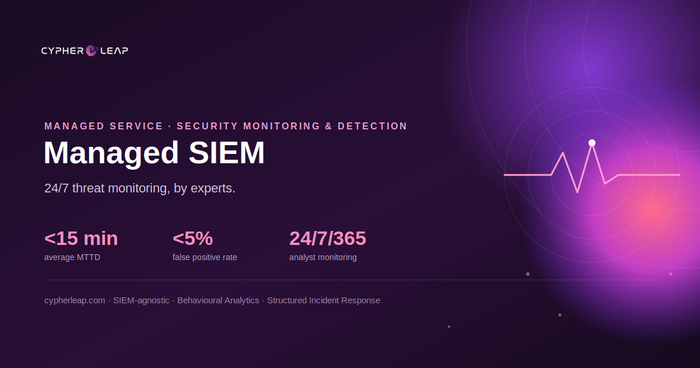
Managed SIEM exists to close the gap most organisations hit when they try to run detection in-house: either the platform is switched on and left to generate noise nobody has time to read, or a small internal team drowns in alert fatigue and misses the signal that actually matters. CypherLeap takes a SIEM-agnostic approach, selecting the right platform from its partner roster for the client's environment, then staffing it with senior analysts providing 24/7/365 monitoring, behavioural analytics tuned to attacker patterns, and correlation rules built to keep false positives down rather than pass every ping straight to the client.
The engagement runs in four phases:
- Environment assessment and SIEM architecture design
- Platform deployment with a two-week baseline tuning period
- An operational handover with documented runbooks and a live team briefing
- Ongoing continuous improvement through monthly threat reviews, quarterly detection tuning, and annual architecture reviews
When something real is found, containment and response happen within minutes under structured escalation with defined SLAs, and the client gets monthly reporting covering detections, incidents, mean time to detect (MTTD), mean time to respond (MTTR), and recommendations, not just a dashboard link.