
Managed GRC (Governance, Risk & Compliance)
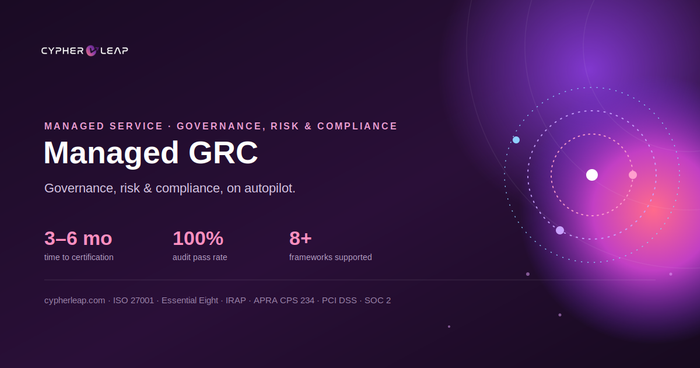
Managed GRC covers the full lifecycle of a compliance program, not just the paperwork. CypherLeap builds a customised ISMS from the ground up, including policies, procedures, standards and guidelines, and maintains a risk register using the ISO 27005 methodology with quarterly reviews. Policies are actively managed through their full lifecycle: drafted, approved, distributed and kept current, not written once and left to go stale. An internal audit program provides annual control coverage with remediation tracked to closure, and compliance evidence is collected automatically through a GRC platform rather than chased manually before every audit season. When it's time for external audit, CypherLeap coordinates the whole process, drawing on a track record it states as a 100% audit pass rate.
The engagement runs in four phases:
- Scoping and gap analysis with a remediation roadmap
- ISMS build and platform configuration
- Audit readiness with mock assessments
- Ongoing management covering annual reviews and adapting the program as regulations change.
CypherLeap supports eight or more frameworks under this service, including ISO 27001:2022, Essential Eight, PCI DSS 4.0, APRA CPS 234, SOC 2, NIST CSF and IRAP, and states a typical time to certification of 3–6 months, backed by a library of 30-plus policy templates. The result is a compliance function that runs continuously in the background rather than one that gets rebuilt from scratch every time an auditor is due.