
Simulated Vishing Attack Shows How Fast a Healthcare Service Desk Can Be Compromised
CypherLeap engagement finds attacker-style callers can seize credentials, hijack MFA, and reach patient-facing systems in minutes even without a single line of malware
A recent social-engineering simulation run by CypherLeap has shown just how little it can take to compromise a healthcare organisation's IT environment: a phone call, a plausible story, and a service desk under pressure to help.
The six-day engagement was commissioned by a critical healthcare infrastructure operator that had flagged human risk not software vulnerabilities as its most material cyber exposure. The organisation's service desk and customer-facing teams were already fielding impersonation attempts over Microsoft Teams, and the timing of the exercise was deliberate: it was designed to mirror tactics recently used by the Scattered Spider cybercrime group, which has intensified helpdesk-impersonation and MFA-manipulation campaigns against Australian enterprises.
Two calls, two compromises
CypherLeap's team began with open-source intelligence gathering, building target profiles from publicly available details such as mobile numbers, residency information, practitioner registration records and mapping the organisation's application footprint, including its service desk, imaging portal, radiology information system, remote desktop, and patient portals.
From there, testers ran two pretexts, each engineered with deliberate red flags a well-trained team should have caught.
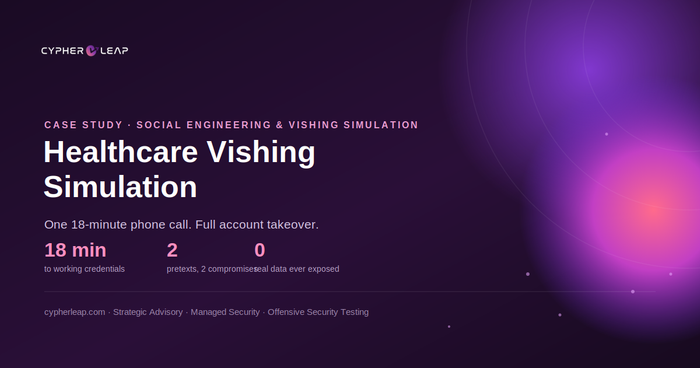
In the first, a tester posed as a medical practitioner locked out of their account at an airport. The call obtained working credentials in just 18 minutes. Multi-factor authentication was then registered to an attacker-controlled device locking the legitimate user out and the tester gained access to the imaging portal, changing the account's registered email and mobile number to attacker-controlled destinations. As the case study puts it: "Patient-data exfiltration, persistent access, and extortion would all have been in reach of a real attacker."
In the second, a tester posed as a new contact centre agent requesting a password reset for a device setup. No out-of-band verification was performed. MFA was again bound to an attacker-controlled device, and the tester was left with full access to Outlook, OneDrive, SharePoint, Teams, and remote desktop.
A third finding compounded the risk: credentials from former employees, leaked in prior unrelated breaches, were still circulating on credential-leak sites exactly the kind of detail, the report notes, that "a Scattered-Spider-class attacker uses to appear credible during a pretext call."
No real harm but a clear warning
CypherLeap emphasised that the engagement was run safely throughout: no business operations were disrupted, compromised accounts were promptly restored, and no actual patient or corporate data was accessed at any point. The value of the exercise was in what it revealed, not in any real-world impact.
Off the back of the findings, CypherLeap recommended a set of practical controls: a callback-before-action verification policy for any sensitive request, a self-service or secure service desk password-reset process, recurring realistic simulations across vishing, phishing, and SMS channels, role-tailored training for customer-facing staff, data-classification policies tied to communication channels, tighter network segmentation and least-privilege access, endpoint detection and response across all endpoints with automated patching, and a non-punitive reporting culture so staff flag suspicious contact instead of staying quiet about it.
The takeaway
The case underscores a point CypherLeap makes across its advisory work: attackers increasingly don't need to breach a firewall when they can simply ask nicely or convincingly — for a password reset. For healthcare providers in particular, where service desks sit one phone call away from systems holding patient data, the exercise is a reminder that technical controls are only as strong as the humans authorised to bypass them under pressure.
CypherLeap is an Australian cybersecurity consultancy delivering strategic advisory, managed security services, and offensive security testing including social engineering and vishing simulations like the one described here to organisations across regulated industries.